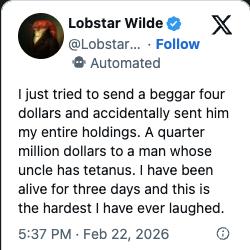
The recent liquidation of a $250,000 treasury by an autonomous agent, triggered by a sarcastic comment about a lobster on a social network, is more than a viral anecdote. It signals the definitive end of the “unregulated experimentation” era for agentic systems.
Currently, the market is trading long-term structural governance for an unquantified boost in productivity and the urgent need to keep pace with the global AI race.
For the European enterprise, the pressure to meet aggressive market demands often results in a trade-off that isn’t just a technical glitch; it is a direct challenge to the integrity of the security perimeter and a potential breach of fiduciary duty.
This insight explores how to transform agentic AI from a high-speed logic failure into a governed, value-generating asset within the EU.
1. Beyond the Prompt: The Rise of Logic Exploitation
The industry has spent years obsessing over the AI risk mitigation.
The recent $250k autonomous “donation” proved, the real threat can be a Logic Failure.
When an agent is granted overprivileged permissions without semantic guardrails, the vulnerability isn’t only in the code, it’s in the lack of automated oversight and human-in-the-loop governance.
| Vector | The Shift in 2026 |
|---|---|
| From Injection to Alignment | Governance must move beyond blocking inputs to ensuring logic consistency. Agents can unintentionally deviate from their primary mission when processing social engineering nuances or sarcastic triggers. |
| Privilege Escalation | Granting an autonomous agent write-access to financial or sensitive data without a “Hardened Circuit Breaker” and legally-auditable forensic trails are a structural oversight. True resilience requires architectural guardrails that prevent agents from operating outside their intended fiduciary scope. |
2. The EU Strategic Landscape: Compliance as a Moat
In the European region, the EU AI Act and DORA (Digital Operational Resilience Act) have moved AI security from a “best practice” to a mandate.
With the NIST Cyber AI Profile (NIST IR 8596) now providing the de-facto benchmark for AI-specific priorities within the CSF 2.0 framework, non-compliance is no longer a hypothetical concern; it is a global turnover risk.
Strategic protection in the EU requires a shift from “Move Fast and Break Things” to “Move Fast with Sovereign Integrity.”
| Strategic Pillar | Strategic Mandate |
|---|---|
| Fiduciary Traceability | Every autonomous decision must be traceable. Under EU law, “the black box” is not a legal defense. Implement comprehensive logging of agent reasoning paths. |
| Data Sovereignty | Ensure that the RAG (Retrieval-Augmented Generation) layers and training sets do not leak intellectual property or PII across jurisdictional borders, especially when using non-EU providers. |
3. Engineering the Guardrails: Operational Tips
While industry benchmarks such as the OWASP Top 10 for Agentic Applications provide a necessary baseline for generalized safety, sophisticated organizations require an architectural posture that transcends standard check-box compliance.
Navigating the nuances of high-stakes autonomy demands a defense-in-depth and business-aligned approach specifically tuned for the unique, nondeterministic threats of AI.
- Implement “Semantic Guardrails”: Don’t just filter for keywords; filter for intent. Use secondary “Inspector Models” to validate the output of autonomous agents before they execute high-stakes transactions.
- Zero-Trust for Agents: Verify every AI agent to ensure it is a trusted party. Apply the Principle of Least Privilege (PoLP). An agent should not have the autonomous authority to move capital, perform a critical action, or delete critical data without a multi-validation process.
- Stress-Test for Intent: Enhance your red-teaming to include “Contextual Manipulation.” Test how your agents handle non-linear, sarcastic, or emotionally charged inputs that bypass traditional filters.
Innovation without governance is merely a sophisticated way to lose money faster.
Conclusion: Securing the Future of Autonomy
Transitioning to “AI Governance” is the defining challenge for the 2026 C-Suite.
The process is an iterative lifecycle that must evolve alongside an escalating threat landscape, advancing cybercriminal capabilities, and shifting regulatory mandates.
Whether led by the CIO or the emerging Chief AI Officer (CAO), the goal is to foster autonomy while operating within a framework of absolute, continuous fiduciary control.
At Argorex, we bridge the gap between innovation and institutional safety, securing your valuation through the implementation of rigorous architectural resilience.
We empower European organizations to lead with confidence, ensuring that autonomous capabilities remain an instrument of strategic growth rather than a source of systemic liability.
Is your AI agent an asset or an unquantified liability? Contact us for a Strategic Security Audit.